

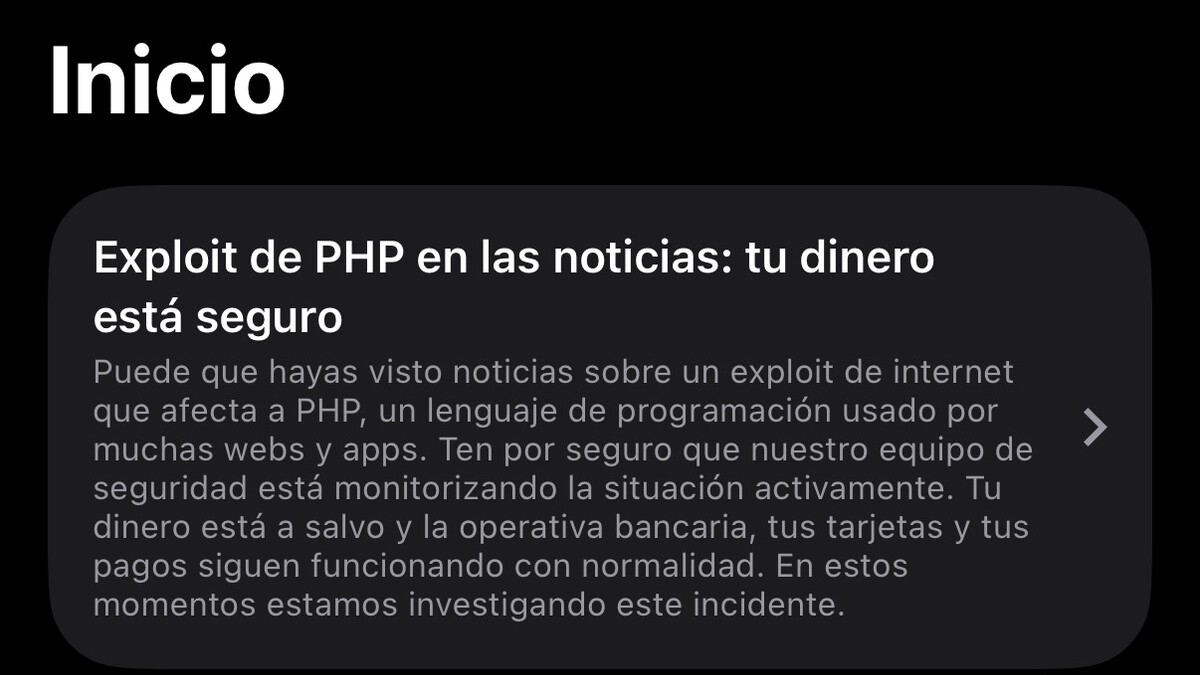
A critical PHP flaw has put half the internet at risk, forcing organizations worldwide to scramble for fixes. Two vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, affect one of the most widely used server-side languages. The fallout is already visible: official websites showing maintenance pages, error messages, and even complete outages.
This isn't a random glitch on a single site. It's the consequence of a deeply embedded technology failing at scale, prompting several organizations to take the drastic step of disconnecting rather than staying exposed.
Find Original, High-end Home Decor that spark conversation at Grand Goldman Shop.
What Happened: PHP Vulnerabilities Exposed
PHP powers a massive share of the web, from small blogs to government portals. The two critical vulnerabilities require immediate patching. Cybersecurity authorities have issued a direct recommendation: update as soon as possible. If updates aren't feasible or temporary mitigations fall short, consider taking systems offline.

That caution has translated into concrete actions in Europe. Administrations and other bodies in the Netherlands, Finland, Denmark, and France have temporarily pulled public websites and services from the internet. The move underscores the severity—governments don't take such steps lightly.

Why PHP Matters: The Invisible Backbone
PHP operates on the server, the part of the internet we never see. When you visit a webpage, PHP often handles the logic that generates the content, interacts with databases, and manages sessions. A flaw here can expose sensitive data or allow attackers to take control.

Because PHP is so ubiquitous, a critical vulnerability has cascading effects. A single exploit can be adapted to target thousands of sites. That's why the response has been swift and, in some cases, drastic.
Who Is Affected and What They Should Do
Any organization running PHP-based applications is potentially at risk. This includes businesses, government agencies, and even individual developers. The first step is to identify whether your systems use affected PHP versions.
If they do, patching is the priority. Most hosting providers and software vendors are releasing updates. For those unable to patch immediately, mitigations like web application firewalls (WAFs) can help, but they are not foolproof. In extreme cases, taking services offline may be the safest option. Anyone following the wider picture can start with Critical PHP Flaw Puts Half the Internet at Risk Worldwide.
Key Takeaways for Website Owners
- Update PHP immediately if you manage a server or application.
- Check with your hosting provider about their patching status.
- Monitor official advisories from cybersecurity agencies for updates.
- Consider temporary mitigations like WAF rules if patching is delayed.
- Have a contingency plan for taking services offline if necessary.
Comparison of Vulnerability Response Steps
| Action | Effectiveness | Urgency |
|---|---|---|
| Apply official patch | High | Immediate |
| Enable WAF rules | Medium | High |
| Take service offline | High (but disruptive) | Critical |
| Monitor advisories | Low (informational) | Ongoing |
What to Watch Next
Expect more organizations to announce patches and possibly temporary shutdowns. The situation is fluid, and authorities are actively monitoring. For businesses, this is a reminder of the importance of timely updates and robust incident response plans. The background to this story is set out in Technology: latest articles. A related thread runs through Jason Molina: The Life and Legacy of a Master of Americana.
The PHP community is working on fixes, but the window of exposure remains. Stay informed through official channels and prioritize security hygiene. Earlier coverage in Indian Court Orders Release of Two Cockroach Movement Leaders shows how the argument developed. A closer look at the same subject appears in Seth Meyers Says 'Nobody Likes' Elon Musk in Late-Night Roast.
FAQ
What are CVE-2026-109618 and CVE-2026-109619?
They are two critical vulnerabilities in PHP that allow attackers to compromise servers. Details are still emerging, but they are severe enough to prompt emergency patches and website shutdowns.
Which countries have taken websites offline?
The Netherlands, Finland, Denmark, and France have seen government and public service websites temporarily removed from the internet as a precaution.
How can I protect my website?
Apply the latest PHP patches immediately. If you can't, use a web application firewall and monitor official advisories. In extreme cases, consider taking your site offline until a fix is applied.
Is my personal data at risk?
If a vulnerable site you use has been compromised, your data could be exposed. Follow news about affected services and change passwords if advised.
Browse the Shop
 Acacia frida deluxe solid wood bed frame |
Bedroom bench |
Bed chest drawers |
Lingerie dresser |
Frame base |
Mirror with jewelry storage |
30 Bathroom Vanity |
Memory foam queen mattress |
Mattresses for back pain |
Nightstand set of 2 |
Grand Goldman Shop |
Civil Lawyer
Deutschland Trikot WM 2026










